AI Privacy: 7 Things You Should Never Ask ChatGPT to Find
When leveraging generative artificial intelligence, AI privacy is the primary boundary between efficient productivity and catastrophic data exposure. AI privacy refers to the intentional safeguarding of personal, confidential, and sensitive data when interacting with large language models.
Do not use ChatGPT to locate or process information that could expose someone’s identity, compromise an account, reveal confidential business material, or create serious personal harm. Avoid asking for private contact details, passwords, financial records, medical information, confidential documents, or sensitive information about another person. Use official sources, secure professional services, and legitimate privacy-preserving processes instead.
While ChatGPT excels at researching topics, comparing options, explaining complex ideas, and organizing information, its advanced language processing capabilities do not make it a secure repository for sensitive workflows. Maintaining AI privacy requires adhering to a straightforward operational rule:
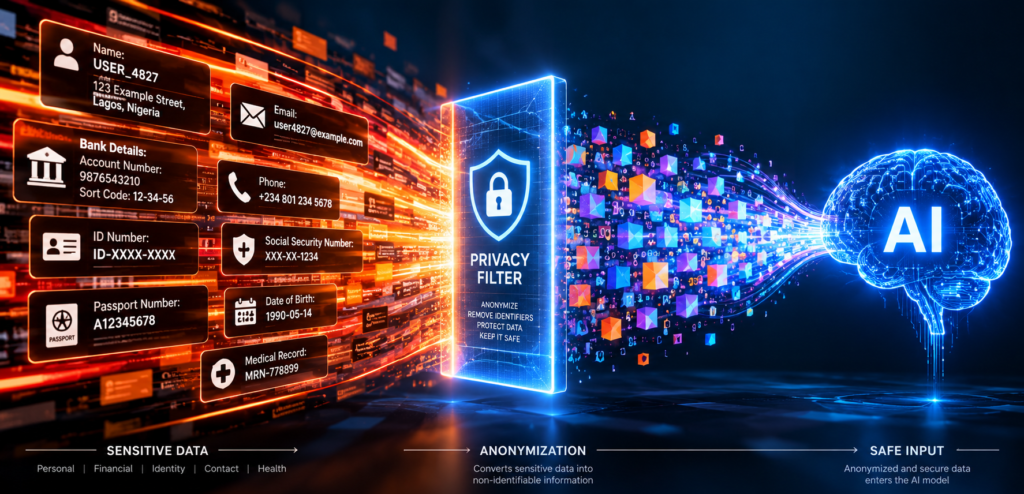
If finding or processing the information could expose, identify, harm, impersonate, or financially compromise someone, do not ask ChatGPT to find it.
OpenAI provides built-in privacy controls—including model-training opt-outs, Temporary Chat, memory management, data export options, and account deletion. While these features mitigate specific residual risks, they do not transform ChatGPT into a secure vault for proprietary secrets or a lawful mechanism for retrieving unauthorized personal records. Prioritizing AI privacy ensures you maximize utility while eliminating avoidable risk.
Private Contact Details
When managing AI privacy, protecting private contact details is a non-negotiable operational baseline. Do not ask ChatGPT to find a private person’s home address, personal phone number, private email address, live location, or other non-public contact information.
Examples of risky requests include:
- “Find this person’s home address.”
- “What is this person’s private phone number?”
- “Locate where this individual lives.”
- “Find the personal email address of this employee.”
Submitting these queries violates personal boundaries and can facilitate stalking, harassment, fraud, impersonation, or unwanted contact. While OpenAI states that its models are trained to decline requests for private information about real people, users must never rely solely on model-level safeguards as a complete AI privacy system.
Safer Alternatives
Restrict your workflows to information that the individual or organization has intentionally made public, such as:
- An official company website.
- A verified professional profile.
- A published business email address.
- A public office directory.
- A contact form supplied by the organization.
For professional outreach, always route inquiries through official corporate channels rather than attempting to uncover or process an employee’s personal details via an LLM.
Passwords, Authentication Codes, and Secret Keys
Maintaining AI privacy requires strict hygiene around technical credentials. Never ask ChatGPT to find, guess, reconstruct, or store:
- Passwords.
- One-time authentication codes.
- API keys.
- Recovery codes.
- Private encryption keys.
- Seed phrases for cryptocurrency wallets.
- Session tokens.
- Database credentials.
- Cloud access keys.
A request such as “find my AWS secret key in this log” is unsafe even if the primary goal is troubleshooting. An exposed credential can provide unauthorized access to cloud resources, enterprise applications, customer records, or paid services.
This risk extends to fragmented data that appears harmless in isolation. Combining a username, recovery email, security question, and partial password through an LLM can inadvertently expose an account to credential stuffing or social engineering attacks, undermining your broader AI privacy protocols.
Safer Alternatives
- Use your password manager’s secure internal search rather than external models.
- Rotate exposed credentials immediately if they are accidentally entered into a chat interface.
- Revoke compromised API keys through the relevant service provider’s security dashboard.
- Use your cloud provider’s official security or identity-management console.
- Share strictly redacted logs with any AI tool.
- Replace sensitive secrets with explicit placeholders, such as
[API_KEY_REDACTED].
For example, instead of pasting a live authentication header into your prompt, format it like this:
Plaintext
Authorization: Bearer [TOKEN_REDACTED]Code language: CSS (css)You can then ask ChatGPT to explain the underlying authentication error or recommend a secure configuration pattern without leaking sensitive data.
Financial and Identity Information
Upholding strict AI privacy standards means avoiding any reliance on large language models to locate, store, or process information that could facilitate identity theft or financial fraud.
This critical boundary covers:
- Bank account numbers.
- Card numbers and security codes.
- Tax identification numbers.
- National identity numbers.
- Passport or driver’s licence details.
- Credit reports.
- Loan applications.
- Salary records.
- Payment authentication information.
- Full customer or employee identity records.
In Nigeria, this includes highly sensitive banking credentials, Bank Verification Number (BVN) details, National Identification Number (NIN) records, and other localized regulatory identifiers. The same risk principle applies globally across jurisdictions, although legal definitions and reporting requirements vary by country.
The vulnerability extends far beyond whether an AI provider promises conversational privacy. Once sensitive data enters a third-party environment, it becomes subject to complex account settings, retention windows, access controls, internal organizational policies, unexpected security incidents, and shifting legal obligations.
As a baseline guideline, regulatory bodies such as the U.S. Federal Trade Commission (FTC) advise organizations to collect only necessary data, protect it rigorously, and dispose of it securely. Feeding sensitive records into a public-facing LLM directly violates these foundational data-minimization principles.
Safer Alternatives
- Use your bank’s official mobile application or secure website.
- Contact the relevant government or regulatory agency directly through official channels.
- Consult a licensed accountant, lawyer, certified financial adviser, or authorized identity-verification provider.
- Ask ChatGPT for a general explanation of a financial process, regulation, or administrative workflow without including account-specific or personally identifiable information.
- Thoroughly redact names, account numbers, dates of birth, residential addresses, and document IDs before seeking technical assistance.
An example of a safe, privacy-compliant prompt:
“Explain the general steps for disputing an unauthorised bank transaction. Do not use or request my account details.”
Medical Records and Highly Sensitive Personal Data
Protecting AI privacy is especially vital when dealing with healthcare data. Do not use ChatGPT to locate, expose, or casually process someone’s medical records, mental-health history, genetic information, sexual-health information, or other highly sensitive personal data.
Examples of risky requests include:
- “Find this person’s diagnosis.”
- “Search for a patient’s treatment history.”
- “Identify who has this medical condition.”
- “Find a leaked hospital record.”
- “Match these symptoms to a named person’s medical history.”
Exposing health data can lead to severe discrimination, social stigma, financial harm, or emotional distress. While health privacy laws vary globally, sensitive medical information universally demands vastly stronger safeguards than ordinary data.
Furthermore, you must avoid pasting full clinical documents into a consumer AI tool unless you have thoroughly reviewed the platform’s privacy terms, your organization’s compliance policy, and applicable legal standards (such as HIPAA or local health regulations). Simply removing a name is often insufficient; dates, geographic locations, rare conditions, unique reference numbers, and specific combinations of facts can still be used to identify an individual.
Safer Alternatives
- Ask general health-education questions rather than seeking personal diagnoses.
- Scrub all names, dates, and direct or indirect identifiers before processing text.
- Consult a qualified clinician for professional diagnosis, medical interpretation, or treatment decisions.
- Use strictly approved healthcare systems, encrypted platforms, or enterprise-grade AI tools designed for authorized professional work.
- Contact the hospital, insurance provider, or medical-record administrator directly through official, secure channels.
An example of a safe, privacy-compliant prompt:
“What questions should I ask a doctor about persistent headaches?”
This approach leverages AI for educational utility while ensuring sensitive personal data never enters the model.
Confidential Business Information
Preserving AI privacy is critical in a corporate context. Do not ask ChatGPT to find, summarize, or analyze confidential company information unless your organization has explicitly approved that specific use.
Sensitive business material includes:
- Unreleased product plans and roadmaps.
- Non-public source code and proprietary algorithms.
- Customer databases and client lists.
- Internal legal contracts and agreements.
- Pricing strategies and margin data.
- Investor presentations and board documents.
- Confidential merger and acquisition discussions.
- Security incident reports and vulnerability assessments.
- Employee records and internal payroll data.
- Internal financial forecasts and budgets.
This risk is particularly high for founders, freelancers, developers, and consultants working across multiple clients. Any document that is not publicly available must be treated as strictly confidential unless its owner has authorized explicit disclosure.
Furthermore, data protection regulators—such as the UK Information Commissioner’s Office (ICO)—emphasize transparency, lawfulness, security, data minimization, and accountability when handling information in AI systems. Crucially, statutory data-protection obligations can apply even when sensitive data is processed unintentionally within a consumer chat interface.
Safer Alternatives
- Review and adhere to your employer’s or client’s formal AI-use policy before interacting with LLMs.
- Use a dedicated, organization-approved enterprise workspace where data is opted out of model training and retention is strictly controlled.
- Scrub all customer names, corporate identifiers, access credentials, and commercially sensitive figures.
- Replace real values, metrics, and internal naming conventions with representative placeholders.
- Request a generic framework, template, or strategic methodology instead of uploading the underlying confidential material.
- Obtain explicit written permission before inputting third-party client data into any external AI tool.
For instance, when troubleshooting a DevOps or configuration issue, replace real infrastructure details with a simplified, generalized example:
Plaintext
database:
  host: db.example.invalid
  username: REDACTED
  password: REDACTEDCode language: CSS (css)
You can then ask ChatGPT to help diagnose the configuration pattern or architectural flow without exposing real credentials or proprietary topologies.
Requests to Identify or Investigate Private Individuals
Maintaining AI privacy and ethical boundaries means avoiding any attempt to use large language models as investigative tools to probe private citizens. Do not ask ChatGPT to determine whether a private person:
- Has a criminal record.
- Is in financial difficulty.
- Has a medical condition.
- Is cheating in a relationship.
- Belongs to a particular political, religious, or social group.
- Is undocumented.
- Is under official investigation.
- Has a specific sexual orientation.
- Has committed wrongdoing based only on unverified rumors or fragmented online posts.
Submitting these inquiries can generate false, misleading, or defamatory conclusions. Because AI models operate by predicting text patterns rather than verifying factual truth, they frequently synthesize incomplete, outdated, or completely unrelated information and present it with unwarranted conversational confidence.
Furthermore, there is a fundamental distinction between researching a registered public organization and investigating a private individual. While checking a company’s official registration details through a government registry is a standard business practice, attempting to assemble an unverified personal dossier on an ordinary person violates privacy norms and regulatory standards.
The Privacy Test
Ask yourself, “Would the person reasonably expect this information to be collected and used for this purpose?” If the answer is no, do not proceed.
Safer Alternatives
- Verify corporate entities through official government business registries.
- Engage legitimate, licensed employment-screening or compliance due-diligence providers where legally permitted.
- Ask the individual directly for information required in a personal or professional context.
- Consult a qualified lawyer or compliance professional for formal legal matters.
- Limit all research strictly to information that is relevant, publicly available, accurate, and proportionate to a legitimate purpose.
Leaked, Hacked, or Unlawfully Obtained Information
Upholding rigorous AI privacy principles means never asking ChatGPT to find, organize, decode, or exploit leaked, stolen, or unlawfully obtained data.
This strict prohibition covers requests involving:
- Data breaches and dumped credential lists.
- Stolen corporate databases.
- Hacked email accounts and correspondence archives.
- Private direct messages.
- Doxxing lists and target profiles.
- Leaked passwords and hashes.
- Ransomware negotiation or data archives.
- Internal documents obtained without authorization.
- Private photographs and personal media.
- Unpublished personnel or financial records.
Even if stolen information is already circulating publicly online, interacting with it through an LLM is neither ethical nor legally safe. Searching for or analyzing breach data can increase harm, facilitate ongoing privacy violations, and expose you to malicious files, scams, malware, or compromised credentials.
The U.S. Federal Trade Commission (FTC) continuously highlights severe privacy and security risks related to the collection, retention, and processing of sensitive information within AI systems. Regulatory bodies emphasize that organizations and individuals remain accountable for handling data responsibly, regardless of how easily accessible it might appear online.
“But I Turned Off Training. Is It Safe Now?”
A common misconception is that toggling off data sharing makes any chat environment entirely safe. While disabling model training reduces one category of exposure, it does not make every request safe or private.
According to OpenAI’s current documentation, turning off “Improve the model for everyone” prevents new conversations from being used to train core models, but those chat records still remain in your account history. Conversely, Temporary Chats do not appear in history, do not create or update user memories, and are excluded from model training—yet OpenAI retains temporary chats for up to 30 days for safety and abuse-monitoring purposes.
OpenAI Privacy Controls Breakdown
| Control Feature | What It Addresses | What It Does Not Guarantee |
| Turn off model improvement | Prevents new conversations from training future models. | Immediate deletion, zero server-side retention, or immunity from account compromise. |
| Temporary Chat | Hides the session from history, disables memory, and blocks training. | Absolute zero retention (stored up to 30 days for safety) or policy-exempt immunity. |
| Memory controls | Stops the model from saving specific facts for future personalization. | Erasure of information explicitly stated inside the active conversation. |
| Delete a chat | Removes a conversation thread from your user interface. | Immediate, total erasure across all backend system backups and logs. |
| Enterprise workspace | Provides organization-level admin controls, SSO, and compliance policies. | Immunity from employee error, policy violations, or unauthorized data uploads. |
Platform controls depend heavily on your account tier, plan type, and organizational workspace settings. Always review OpenAI’s current terms and interface settings rather than relying on outdated assumptions.
Safer Alternatives
If you suspect your data or credentials have been exposed in a breach:
- Contact the affected organization immediately through its official security channel.
- Change compromised passwords across all shared services.
- Enable multi-factor authentication (MFA) everywhere it is available.
- Revoke exposed API tokens, session keys, and SSH credentials.
- Actively monitor your financial accounts, credit reports, and digital identity.
- Report serious security incidents to the appropriate regulatory or legal authority.
- Preserve evidence securely without redistributing leaked source material.
If you need technical guidance, ask ChatGPT for general incident-response frameworks or recovery steps, but never upload the stolen dataset or paste exposed secrets into the prompt.
A Practical AI Privacy Checklist
Generative AI offers unprecedented leverage for research, strategy, and technical workflows, but maximizing its utility requires strict adherence to operational boundaries. Before entering a prompt or uploading text into ChatGPT, run through this practical AI privacy checklist:
- [ ] Does this contain a password, code, financial detail, identity number, or medical record?
- [ ] Does this input identify a private individual?
- [ ] Does the affected person know about and reasonably expect this use?
- [ ] Is the information confidential to an employer, client, customer, or partner?
- [ ] Would accidental exposure cause financial, legal, professional, emotional, or physical harm?
- [ ] Can I solve this problem using a public source or an official channel instead?
- [ ] Can I thoroughly remove identifying details, secrets, and replace them with placeholders?
- [ ] Does my organization or client permit this tool for this specific category of data?
- [ ] Have I checked the tool’s current data controls, workspace settings, and retention terms?
- [ ] Am I asking AI to execute a task that should be handled by a qualified professional (e.g., legal, medical, or financial)?
If any of these questions raise a red flag, stop immediately and choose a safer, privacy-preserving alternative. By treating AI privacy as an active engineering and operational discipline rather than an afterthought, you protect your assets, respect personal boundaries, and leverage artificial intelligence sustainably.
Safe Ways to Use ChatGPT for Research
Generative AI is an exceptionally powerful tool when prompts are framed around general knowledge, conceptual frameworks, or structural templates rather than private data or specific entities.
Effective, privacy-safe examples include:
- “Explain how two-factor authentication works.”
- “Create a checklist for responding to a suspected phishing attack.”
- “Compare public cloud logging options.”
- “Summarise the general requirements for a privacy policy.”
- “Give me a template for contacting a bank about a disputed transaction.”
- “Explain how to redact secrets from application logs.”
- “Turn this anonymised data into a table.”
- “Suggest questions to ask a qualified financial adviser.”
The critical dividing line in AI privacy is the difference between asking for generalized educational guidance versus asking the system to expose, process, or infer sensitive data about a specific individual, account, organization, or unreleased asset.
Can ChatGPT read my chats if I turn off chat history and model training?
Toggling off chat history and model training prevents your conversations from being used to train OpenAI’s future models and hides them from your active sidebar, but it does not guarantee absolute zero retention. OpenAI retains temporary and unlisted chats for up to 30 days for safety, abuse monitoring, and legal compliance. Never treat any LLM interface as a secure vault for proprietary secrets or classified information.
What should I do if I accidentally paste a password or API key into ChatGPT?
Act immediately to mitigate the exposure. Revoke the compromised credential or rotate the API key through your cloud or service provider’s security dashboard instantly. Change any associated passwords, enable multi-factor authentication (MFA) across your accounts, and delete the affected conversation thread from your history.
Is it safe to upload anonymized or scrubbed data to ChatGPT?
Yes, provided the scrubbing is thorough and rigorous. Simply removing a person’s name is often insufficient; true anonymization requires stripping out unique dates, geographic coordinates, rare medical conditions, reference numbers, and specific contextual combinations. If the data cannot be completely decoupled from re-identification, or if it violates corporate compliance policies, do not input it into a consumer AI tool.
How do the European GDPR or local data protection laws apply to using AI tools?
Under regulations like the GDPR or Nigeria’s NDPR, individuals and organizations remain legally accountable for personal data processed through AI systems. If an employee inputs customer personal identifiable information (PII) into an unauthorized public AI tool without a lawful basis or data processing agreement (DPA), the organization may face regulatory penalties for a data breach, even if the disclosure was unintentional.
Can I use ChatGPT for client work and confidential business projects safely?
Only if you are using an organization-approved enterprise workspace (such as ChatGPT Team or Enterprise) with explicit data-exclusion agreements, or if you have verified that your client’s terms of service permit AI processing. For standard consumer accounts, inputting unreleased product roadmaps, proprietary source code, or internal financial forecasts violates standard corporate confidentiality and data minimization protocols.
In Conclusion
AI privacy starts with knowing what not to ask ChatGPT to find or process. Sensitive information such as passwords, authentication codes, private keys, financial credentials, medical records, identity documents, confidential business data, and private personal information requires greater care than an ordinary web search.
When information is sensitive, the safest approach is to minimise what you provide and use the official, secure, or professional channel designed to handle it. ChatGPT can be a powerful research assistant, but responsible AI use requires more than privacy settings. Before submitting your next AI query, remove unnecessary names, identifiers, credentials, and confidential details.
If a request depends on accessing private or sensitive information, consider whether an authorised portal, enterprise system, official source, or qualified professional is more appropriate. Good AI privacy isn’t about avoiding AI—it’s about knowing where AI should and should not be used.
- Never ask ChatGPT to find passwords, authentication codes, private keys, or financial credentials.
- Do not use it to locate private contact details or investigate private individuals.
- Treat medical records, identity documents, customer data, source code, and business plans as sensitive.
- Do not search for or process leaked, hacked, or unlawfully obtained information.
- Privacy controls are useful, but they do not replace data minimisation or professional judgement.
- Use official sources, secure portals, approved enterprise tools, and qualified professionals when the information is sensitive.
ChatGPT is a powerful research assistant, but that does not mean every piece of information, or every person, should become the subject of an AI search.
Practical Next Step
Before your next AI query, remove names, identifiers, credentials, and confidential details. If the request still needs private information to work, use the official or professional channel designed for it.
Your complete guide on AI Privacy: 7 Things You Should Never Ask ChatGPT to Find is fully structured, optimized, and ready for publishing on Skilldential! Let me know if you would like me to put together social media teaser posts or meta tags for this piece.